Chapter 80 — Secure AI Platform Product Engineering & Feature Architecture
80.1 Introduction
A technically advanced AI platform can still fail if its features are poorly designed.
Product engineering connects:
user needs
business requirements
UX
AI capabilities
security
reliability
performance
cost
compliance
operational readiness
For an AI media platform, this becomes especially important because a single feature may involve multiple systems.
For example, an AI image generation feature can involve:
User
 ↓
Frontend
 ↓
Authentication
 ↓
Authorization
 ↓
Prompt validation
 ↓
Usage/quota check
 ↓
Job creation
 ↓
Queue
 ↓
Model routing
 ↓
AI inference
 ↓
Output validation
 ↓
Object storage
 ↓
Database
 ↓
Result delivery
Therefore, a feature is not simply a button on a screen.
A production feature is a complete system capability with defined behavior, security boundaries, costs, failure modes, and operational requirements.
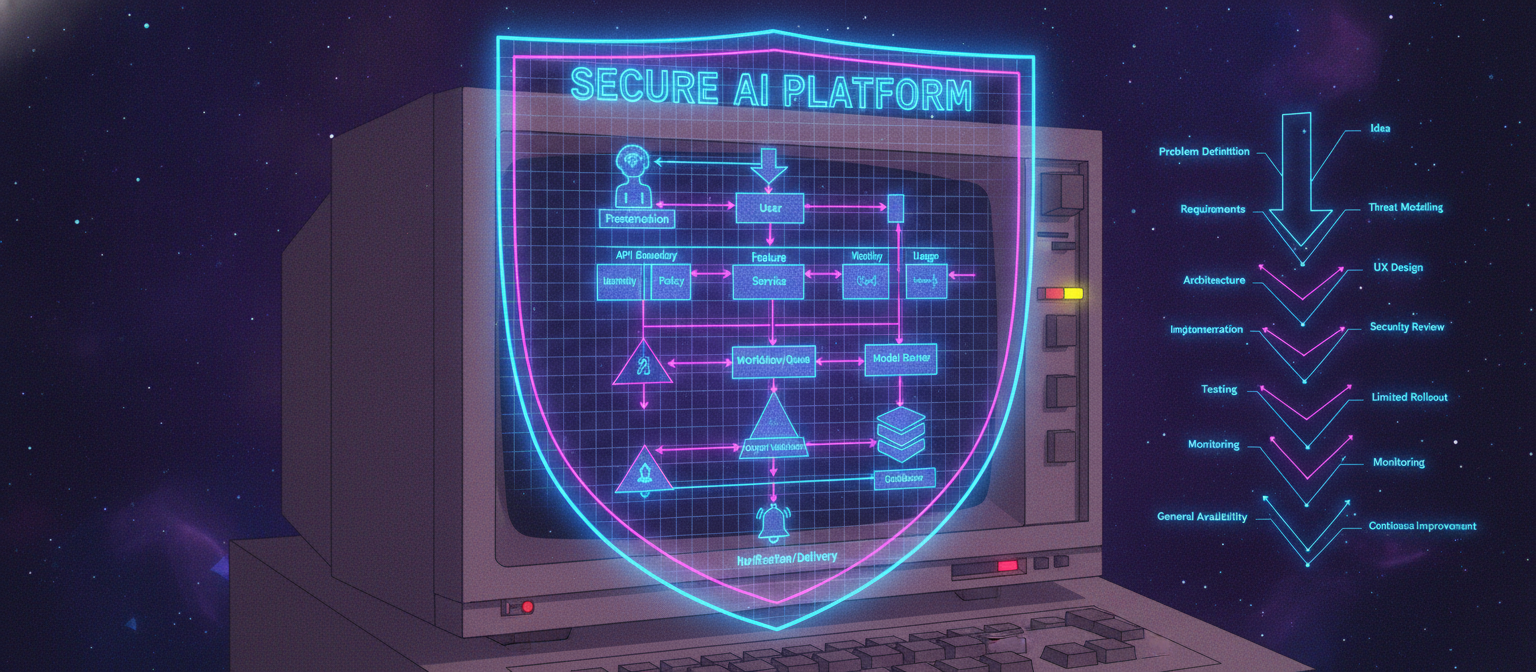
80.2 Feature Engineering Lifecycle
A mature feature lifecycle can be represented as:
Idea
 ↓
Problem Definition
 ↓
Requirements
 ↓
Threat Modeling
 ↓
UX Design
 ↓
Architecture
 ↓
Implementation
 ↓
Testing
 ↓
Security Review
 ↓
Limited Rollout
 ↓
Monitoring
 ↓
General Availability
 ↓
Continuous Improvement
 ↓
Retirement
Skipping stages can create expensive problems later.
80.3 Start With the User Problem
A feature should begin with a problem rather than technology.
Weak approach:
“We have an AI model, so let's add an AI button.”
Better approach:
“Users need to remove backgrounds from product photos quickly without manually selecting complex edges.”
The second statement provides a measurable product objective.
80.4 Product Requirements
Requirements should describe expected behavior.
A feature specification might define:
Functional requirements
user can upload an image
user can select background removal
system processes the image
system returns a preview
user can export the result
Non-functional requirements
authorization required
maximum file size enforced
processing timeout defined
private media protected
processing cost controlled
audit events recorded
80.5 Acceptance Criteria
Every feature should have explicit acceptance criteria.
For example:
Given an authenticated user
When they upload a supported image
Then the system validates the file
And creates a processing job
And displays job progress
And stores the resulting asset privately
And only authorized users can access it.
Acceptance criteria transform vague requirements into testable behavior.
80.6 AI Feature Design
AI features require additional requirements.
A feature specification may include:
Input
 ↓
Validation
 ↓
Policy checks
 ↓
Model selection
 ↓
Inference
 ↓
Output validation
 ↓
Storage
 ↓
User presentation
The system should define what happens when any stage fails.
80.7 AI Feature Failure Modes
Possible failures include:
invalid input
unsupported file
provider unavailable
model timeout
unsafe output
low-quality output
quota exceeded
storage failure
database failure
queue failure
network failure
Each failure should have an intentional user-facing outcome.
80.8 Safety-by-Design
Safety should be built into the feature rather than added afterward.
For an AI image feature, controls might include:
Input
 ↓
Authentication
 ↓
Authorization
 ↓
Policy validation
 ↓
AI processing
 ↓
Output validation
 ↓
Safe delivery
Security and safety decisions should occur at appropriate trust boundaries.
80.9 Feature Threat Modeling
Before implementation, identify:
Assets
What must be protected?
Examples:
user media
prompts
generated media
API credentials
billing information
personal data
Actors
Who interacts with the feature?
normal users
administrators
automated clients
attackers
compromised accounts
Threats
Examples:
unauthorized access
prompt injection
malicious uploads
resource exhaustion
data leakage
cross-tenant access
account abuse
Controls
For each threat, define preventive and detective controls.
80.10 UX and Security
Security controls should be understandable to users.
For example, instead of displaying:
HTTP 403
the interface could explain:
“You don't have permission to access this project.”
Similarly:
Quota exceeded
could become:
“You've reached today's generation limit. Try again tomorrow or review your plan.”
Good UX reduces confusion without exposing sensitive internal information.
80.11 Progressive Disclosure
Complex AI applications should not expose every advanced option immediately.
A useful interface can start with:
Prompt
Upload
Generate
and provide advanced options such as:
resolution
aspect ratio
model
style
quality
seed
negative constraints
processing priority
through an advanced settings section.
This reduces cognitive load.
80.12 Feature Flags
Feature flags allow functionality to be enabled or disabled without requiring a complete redeployment.
Conceptually:
Feature flag
      |
      +-- OFF → Feature unavailable
      |
      +-- ON  → Feature enabled
More advanced flags can target:
specific environments
user groups
plans
regions
internal testers
percentage of traffic
Feature flags are useful for controlled rollout.
80.13 Secure Feature Flags
Feature flags should not be treated as client-side security controls.
A user should not be able to modify browser state and activate an unauthorized premium capability.
Therefore:
Browser flag
may control UI presentation, but:
Server-side entitlement check
must enforce actual authorization.
80.14 Entitlements
Feature availability should be determined from server-side policy.
Conceptually:
User
 ↓
Plan
 ↓
Entitlements
 ↓
Feature access
 ↓
Usage quota
For example:
Free
 ├── Basic editing
 └── Limited generation

Standard
 ├── Higher limits
 └── Additional models

Premium
 ├── Advanced models
 ├── Higher resolution
 └── Priority processing
The exact plans should be determined by the product strategy.
80.15 Experimentation
Not every product decision should be based on assumptions.
Controlled experiments can compare:
UI designs
onboarding flows
generation workflows
pricing presentation
model routing
default settings
The experiment should define:
hypothesis
population
control
variant
metrics
duration
stopping conditions
80.16 A/B Testing
An A/B experiment might look like:
Users
  |
  +---- Group A → Interface A
  |
  +---- Group B → Interface B
Measure outcomes such as:
task completion
generation success
retention
latency
error rate
conversion
Security-sensitive behavior should not be weakened merely to improve experimental metrics.
80.17 Experiment Safety
Experiments should have guardrails.
For example:
Experiment
   |
   +-- Performance threshold
   +-- Error threshold
   +-- Safety threshold
   +-- Cost threshold
   +-- Rollback condition
If the experiment exceeds a predefined threshold, it should automatically or operationally stop.
80.18 Canary Releases
A new feature can initially be released to a small percentage of traffic.
For example:
100% existing version
       ↓
95% existing
5% new
       ↓
90% existing
10% new
       ↓
50% existing
50% new
       ↓
100% new
At each stage, monitor:
errors
latency
security alerts
AI quality
cost
user behavior
80.19 Rollback
Every significant feature should have a rollback strategy.
Rollback may mean:
disabling a feature flag
reverting application code
restoring a previous model
switching AI provider
disabling an expensive processing mode
For database changes, rollback may be more complicated.
Therefore schema changes should be designed for safe migration.
80.20 Feature Versioning
AI behavior can change as models evolve.
A generated result may depend on:
Model version
Prompt version
Safety policy version
Processing pipeline version
Feature version
Recording these versions improves:
reproducibility
debugging
auditability
rollback
quality analysis
80.21 Prompt Versioning
Prompts should be treated as production configuration.
Instead of silently modifying a prompt, maintain versions:
Prompt v1
Prompt v2
Prompt v3
Generation records can then reference the prompt version used.
This allows teams to investigate:
Why did output quality change after the latest deployment?
80.22 Model Versioning
Similarly:
Model A v1
Model A v2
Model B v1
should be tracked.
A generation record might conceptually contain:
generation_id
model_id
model_version
prompt_version
policy_version
created_at
This supports reproducibility.
80.23 AI Quality Metrics
Traditional software metrics are not enough.
AI features may also require:
accuracy
relevance
visual quality
instruction following
hallucination rate
safety violation rate
refusal correctness
latency
consistency
Different AI features require different evaluation criteria.
80.24 Human Evaluation
Automated metrics cannot always determine whether an AI-generated result is useful.
Human reviewers may evaluate:
quality
relevance
safety
usefulness
visual correctness
Human evaluation should use clear rubrics to reduce subjective inconsistency.
80.25 Automated Evaluation
Automated evaluation can run continuously.
For example:
New model
 ↓
Evaluation dataset
 ↓
Quality tests
 ↓
Safety tests
 ↓
Latency tests
 ↓
Cost tests
 ↓
Decision
Only models meeting defined thresholds should progress to production.
80.26 Feature Telemetry
Each feature should generate useful telemetry.
Examples:
feature_started
feature_completed
feature_failed
generation_queued
generation_started
generation_completed
generation_rejected
export_completed
Events should avoid unnecessary sensitive data.
80.27 Product Analytics vs. Security Logs
These systems serve different purposes.
Product analytics
Measures:
feature usage
engagement
conversion
retention
Security logs
Measure:
authentication events
authorization failures
suspicious behavior
policy violations
administrative actions
They can share infrastructure, but their purposes and retention requirements should remain clearly defined.
80.28 Privacy-Preserving Product Analytics
AI applications may process highly sensitive user content.
Analytics should avoid unnecessarily collecting:
full prompts
private media
document contents
personal identifiers
Instead, use:
feature_id
event_type
timestamp
coarse metadata
anonymous/pseudonymous identifier
where sufficient for the product objective.
80.29 Feature Cost Monitoring
Every expensive feature should have a cost profile.
Track:
Usage
 ×
Average cost per operation
 =
Estimated feature cost
Monitor actual values after launch.
A feature that unexpectedly becomes popular can otherwise create a significant infrastructure bill.
80.30 Feature Reliability
Track:
success rate
failure rate
timeout rate
cancellation rate
queue delay
provider failures
processing duration
A feature should have its own reliability objectives where appropriate.
80.31 Feature-Level SLOs
For example:
AI generation submission:
99.9% successfully accepted

Preview generation:
95% completed within target

Result retrieval:
99.9% available
Exact targets should reflect product requirements.
80.32 Graceful Degradation
An AI feature should define what happens when resources are limited.
For example:
Preferred model
 ↓
Fallback model
 ↓
Lower resolution
 ↓
Queue request
 ↓
Temporarily unavailable
The user should receive clear status information rather than an indefinite loading screen.
80.33 Cancellation
Long-running jobs should support cancellation where practical.
A cancelled job should transition to an explicit state:
RUNNING
   ↓
CANCEL_REQUESTED
   ↓
CANCELLED
Workers should respect cancellation signals when safe.
Already-completed work should not necessarily be treated as reversible.
80.34 Idempotency
Expensive operations should avoid accidental duplicate execution.
For example, a user double-clicking:
Generate
Generate
should not necessarily create two expensive jobs.
An idempotency key can conceptually associate repeated requests with the same operation.
This reduces:
duplicate processing
duplicate billing
duplicate storage
unnecessary AI costs
80.35 Feature State Machines
Complex AI features benefit from explicit state models.
Example:
CREATED
   ↓
VALIDATING
   ↓
QUEUED
   ↓
RUNNING
   ↓
POST_PROCESSING
   ↓
VALIDATING_OUTPUT
   ↓
SUCCEEDED
Failure paths can include:
FAILED
CANCELLED
EXPIRED
REJECTED
Explicit state machines reduce ambiguous behavior.
80.36 Notifications
Long-running operations can notify users when complete.
Possible channels include:
in-app notifications
email
push notifications
Notifications should not reveal sensitive content to unintended recipients.
For example, an email should not necessarily contain a private generated image directly if the recipient's identity cannot be reliably verified.
80.37 Export and Sharing
Sharing is a particularly important security boundary.
Private media should default to:
Private
rather than:
Public
If users intentionally share content, the system should clearly communicate:
80.38 Feature Documentation
Every production feature should have documentation covering:
purpose
inputs
outputs
limitations
supported formats
quotas
failure behavior
privacy behavior
security controls
cost implications
Internal documentation should additionally cover:
architecture
dependencies
operational procedures
alerts
rollback
troubleshooting
80.39 Production Readiness Review
Before general availability, evaluate:
Product
Engineering
Security
AI
Operations
Cost
80.40 Feature Lifecycle Management
Features should not exist forever simply because they were once released.
A mature lifecycle is:
Experimental
     ↓
Beta
     ↓
General Availability
     ↓
Mature
     ↓
Maintenance
     ↓
Deprecated
     ↓
Retired
Retirement can reduce:
maintenance burden
security exposure
infrastructure cost
operational complexity
80.41 Deprecation
Users should receive appropriate notice before important functionality is removed.
Deprecation planning may include:
announcement
migration guidance
replacement feature
timeline
telemetry
final shutdown
Deprecated APIs should not remain indefinitely without ownership.
80.42 Feature Dependencies
Features often depend on other services.
For example:
AI Image Generation
 ├── Authentication
 ├── Billing
 ├── Queue
 ├── Model Provider
 ├── Object Storage
 ├── Database
 └── Notification
Dependency mapping helps identify what happens if one component fails.
80.43 Dependency Failure Design
A feature should define dependency-specific behavior.
For example:
Database unavailable
→ reject new job creation safely

AI provider unavailable
→ switch provider or queue job

Storage unavailable
→ do not claim successful completion

Notification unavailable
→ generation can still complete
   if notification is non-critical
This prevents secondary failures from corrupting feature state.
80.44 Avoiding Feature Coupling
Highly coupled features become difficult to modify.
For example, directly embedding payment logic inside every AI worker can create unnecessary dependencies.
A cleaner architecture might use:
Feature
 ↓
Entitlement Service
 ↓
Usage Service
 ↓
AI Service
Each service has a defined responsibility.
80.45 Product Security Review
Security should participate before launch for high-risk features.
Review questions include:
What data does the feature access?
Which users can invoke it?
Which tenants can access the resulting data?
What external services receive data?
What expensive resources can it consume?
What happens when authorization changes?
What happens when a user deletes their data?
What happens when the feature fails?
80.46 AI Feature Launch Checklist
A practical launch sequence is:
Requirements
 ↓
Architecture
 ↓
Threat model
 ↓
Prototype
 ↓
Evaluation
 ↓
Security testing
 ↓
Performance testing
 ↓
Cost testing
 ↓
Internal release
 ↓
Canary
 ↓
Limited beta
 ↓
General availability
 ↓
Continuous monitoring
80.47 Final Feature Architecture
A production AI feature can be viewed as:
                    User
                      |
                 Presentation
                      |
                API Boundary
                      |
        +-------------+-------------+
        |             |             |
     Identity      Policy        Usage
        |             |             |
        +-------------+-------------+
                      |
                Feature Service
                      |
              Workflow/Queue
                      |
                Model Router
                      |
             AI Inference Layer
                      |
              Output Validation
                      |
                Object Storage
                      |
                 Database
                      |
            Notification/Delivery
                      |
                Observability
Every layer contributes to the final user experience.
80.48 Final Principle
A feature should not be considered complete merely because its main function works.
A production-ready AI feature must also answer:
Who can use it?
What can they provide?
What data does it access?
What does it cost?
What happens when it fails?
How is it monitored?
How is it secured?
How is it scaled?
How can it be rolled back?
How can it eventually be retired?
This is the difference between a prototype and a production platform.
80.49 Conclusion
Secure product engineering brings together the architectural disciplines developed throughout the previous chapters.
A mature AI platform should build features through a controlled lifecycle:
define the user problem
establish requirements
design UX
threat-model the feature
define authorization
design AI safety controls
implement explicit state transitions
measure quality
measure performance
measure cost
test failure modes
release gradually
monitor continuously
maintain rollback capability
deprecate responsibly
The central principle is:
Every AI feature should be treated as a complete production system capability—not merely as a UI component or model call.
When product engineering, security, AI safety, reliability, performance, and FinOps are designed together, new capabilities can be introduced faster without turning the platform into an uncontrolled collection of fragile features.



Comments
Post a Comment