97.1 Introduction
A technically strong security architecture can still fail if the organization cannot operate it consistently.
Security program management provides the organizational structure required to transform security architecture into sustained operational capability.
It answers questions such as:
Who owns each security control?
Who approves security exceptions?
How are security priorities selected?
How often are risks reviewed?
How are security projects tracked?
How are incidents escalated?
How are new AI capabilities evaluated?
How is security performance measured?
How are lessons converted into improvements?
The objective is to create a repeatable management system:
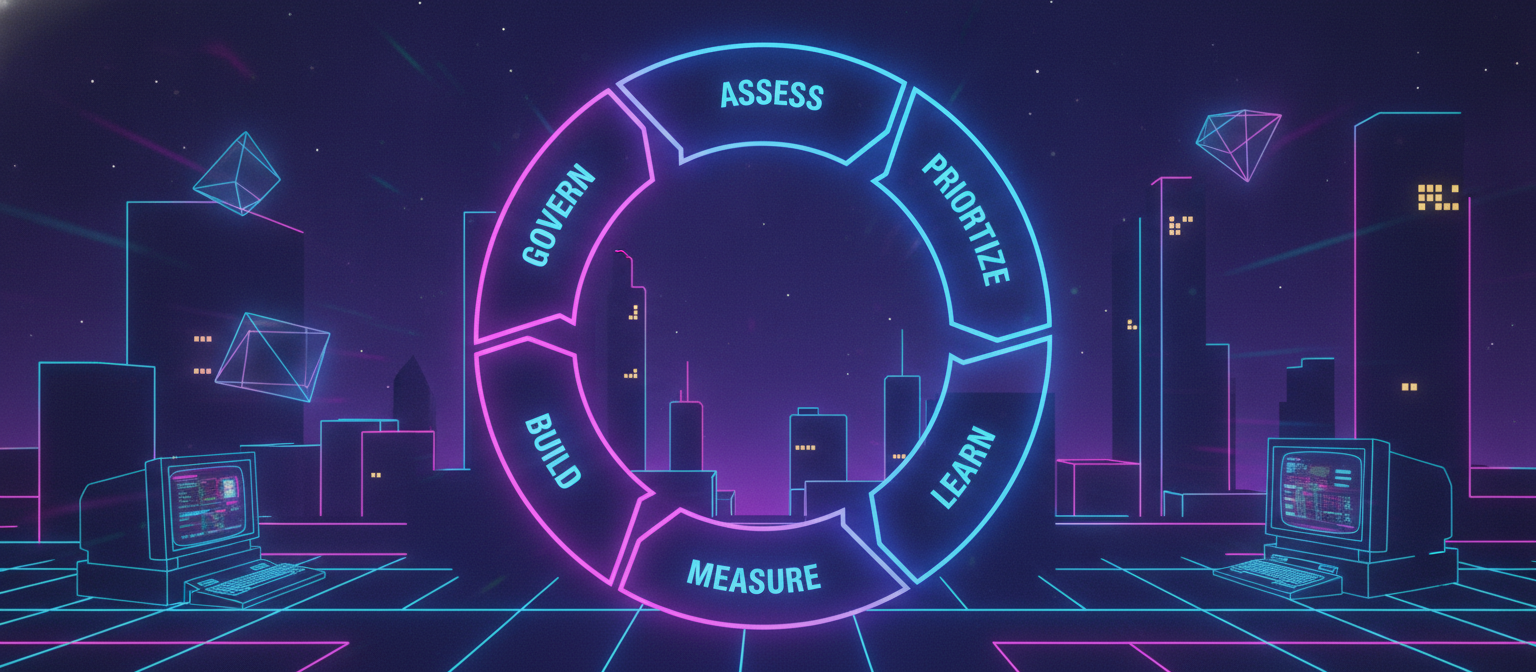
Strategy → Risk → Roadmap → Ownership → Execution → Measurement → Review → Improvement
97.2 Security Program Definition
A security program is the coordinated set of:
used to manage security risk.
For an AI platform, the program must cover both traditional technology security and AI-specific security.
97.3 Security Program Scope
The program should normally cover:
Identity
authentication,
authorization,
privileged access,
account lifecycle.
Application
Infrastructure
cloud,
containers,
Kubernetes,
networking,
runtime security.
Data
classification,
encryption,
retention,
privacy,
access control.
AI
models,
prompts,
agents,
tools,
RAG,
AI safety,
model evaluation.
Operations
monitoring,
detection,
incident response,
recovery.
Governance
policies,
risk management,
compliance,
evidence,
security accountability.
97.4 Security Program Charter
A formal security program should begin with a charter.
The charter should define:
Purpose
Scope
Objectives
Authority
Responsibilities
Risk Appetite
Governance Structure
Reporting
Review Frequency
Escalation Paths
The charter establishes why the program exists and who has authority to make security decisions.
97.5 Security Strategy
A security strategy should align with the platform's business and technical strategy.
For example, if the platform plans to introduce:
then the security strategy must anticipate the associated risks.
Security should not be designed only after the product roadmap is finalized.
97.6 Security Roadmap
A security roadmap converts strategy into executable initiatives.
Example:
Security Strategy
      ↓
Risk Assessment
      ↓
Priority Areas
      ↓
Security Initiatives
      ↓
Milestones
      ↓
Owners
      ↓
Target Dates
      ↓
Validation
Every major initiative should have a measurable outcome.
97.7 Roadmap Categories
A roadmap can be divided into:
Immediate
Address urgent exposure.
Examples:
Near-Term
Improve important security capabilities.
Examples:
centralized logging,
stronger authentication,
security testing,
policy enforcement.
Strategic
Build long-term security architecture.
Examples:
zero-trust architecture,
mature AI security,
continuous validation,
advanced resilience.
97.8 Security Roadmap Prioritization
Roadmap items should be prioritized using:
A useful principle is:
Fix the highest-impact security weaknesses before optimizing lower-impact security capabilities.
97.9 Control Ownership
Every security control should have a clear owner.
For example:
| Control | Primary Owner |
|---|
| MFA | Identity team |
| API authorization | Application/platform team |
| Container security | Infrastructure team |
| AI model evaluation | AI security/AI engineering |
| Data retention | Data governance |
| Security monitoring | SOC/Security Operations |
| Incident response | Incident Response |
| Backup validation | Infrastructure/Resilience |
| Dependency security | Engineering |
| Security policy | Security leadership |
Ownership should be explicit.
97.10 RACI Model
A RACI model can clarify responsibility.
Responsible
Performs the work.
Accountable
Owns the outcome.
Consulted
Provides expertise.
Informed
Receives updates.
For a critical control, there should be no ambiguity about who is accountable.
97.11 Control Ownership Lifecycle
Control ownership should cover:
Design
 ↓
Implementation
 ↓
Operation
 ↓
Monitoring
 ↓
Testing
 ↓
Remediation
 ↓
Retirement
A team that owns only implementation but not ongoing operation does not truly own the control.
97.12 Security Governance Layers
A mature organization can use several governance levels.
Strategic
Executive leadership.
Focus:
risk appetite,
major investments,
strategic risk.
Tactical
Security and technology leadership.
Focus:
roadmap,
priorities,
control effectiveness.
Operational
Engineering and security teams.
Focus:
vulnerabilities,
incidents,
deployments,
daily controls.
97.13 Governance Cadence
Security governance should occur at predictable intervals.
Daily
Weekly
Monthly
security KPI/KRI review,
roadmap status,
exceptions,
control health.
Quarterly
enterprise risk review,
strategic roadmap review,
security investment review,
major architecture changes.
Annually
97.14 Security Steering Committee
A security steering committee can coordinate major decisions.
Possible participants:
security leadership,
engineering leadership,
infrastructure leadership,
product leadership,
privacy/legal representatives where appropriate,
AI leadership,
business representatives.
Its responsibilities may include:
reviewing major risks,
approving priorities,
resolving cross-team ownership conflicts,
reviewing major incidents,
approving strategic security initiatives.
97.15 Security Architecture Review Board
Large architectural changes should receive security review.
Examples:
introducing an AI agent,
adding a new model provider,
exposing a new API,
changing tenant architecture,
changing authentication,
introducing a new storage provider.
The review should identify:
97.16 Security in Product Development
Security should be integrated into the product lifecycle.
A mature lifecycle looks like:
Idea
 ↓
Threat Modeling
 ↓
Security Requirements
 ↓
Architecture Review
 ↓
Implementation
 ↓
Security Testing
 ↓
Release Approval
 ↓
Monitoring
 ↓
Post-Release Review
This is more effective than treating security as a final inspection.
97.17 Security Requirements
Each major feature should define security requirements before implementation.
Example for an AI image-generation feature:
This prevents security requirements from being forgotten during development.
97.18 AI Feature Security Review
AI features deserve dedicated review because they can introduce unique risks.
Questions should include:
What model is used?
What data reaches the model?
Can users influence system prompts?
Can retrieved content influence behavior?
Can the model invoke tools?
What permissions do tools have?
What outputs are trusted?
What monitoring exists?
What happens when the model behaves unexpectedly?
97.19 Security Gates
Security gates should exist at important lifecycle stages.
Examples:
Development gate
code scanning,
secret scanning.
Build gate
dependency checks,
artifact verification.
Deployment gate
AI release gate
model security evaluation,
prompt-injection testing,
safety regression tests.
Production gate
monitoring,
rollback readiness,
incident ownership.
97.20 Security Exception Governance
Security exceptions should follow a controlled process.
Required fields may include:
Exception
Risk
Reason
Owner
Compensating Control
Approval
Created
Expiration
Review Date
Remediation Plan
Exceptions should not become permanent undocumented workarounds.
97.21 Security Decision Records
Important security decisions should be documented.
Examples:
why a particular identity architecture was selected,
why a model provider was approved,
why a risk was accepted,
why a control was temporarily bypassed.
A short decision record can preserve organizational knowledge.
97.22 Architecture Decision Records
Security-related architecture decisions can use ADRs.
A useful structure is:
Title
Context
Problem
Options
Decision
Security Impact
Risk
Alternatives
Consequences
Review Date
This creates historical traceability.
97.23 Security Policy Management
Policies should be:
clear,
applicable,
enforceable,
measurable,
reviewed periodically.
Examples:
access-control policy,
secure-development policy,
AI usage policy,
data-protection policy,
incident-response policy,
vulnerability-management policy.
A policy that cannot be implemented or measured is unlikely to be effective.
97.24 Policy-to-Control Mapping
Policies should map to technical and organizational controls.
Example:
Policy:
Least Privilege
      ↓
Controls:
RBAC
ABAC
Privileged Access Management
Access Reviews
Audit Logging
      ↓
Metrics:
Privilege Violations
Review Completion
Unused Permissions
This creates traceability from policy to implementation.
97.25 Control-to-Evidence Mapping
Each important control should have evidence showing that it operates.
Examples:
MFA
Evidence:
configuration,
enrollment reports,
authentication logs.
Backup
Evidence:
Vulnerability management
Evidence:
scan results,
remediation records.
AI security
Evidence:
97.26 Continuous Control Monitoring
Controls should be monitored continuously where practical.
Examples:
privileged accounts,
encryption status,
exposed services,
expired certificates,
security agents,
configuration policies.
Continuous monitoring can identify control degradation before an incident occurs.
97.27 Control Drift
A control may gradually become ineffective.
Examples:
a new service is deployed without monitoring,
a privileged account receives additional permissions,
a firewall rule is added without review,
a new AI model bypasses the security evaluation pipeline.
Security governance should therefore track control drift.
97.28 Security Program Metrics
The security program itself should have KPIs.
Examples:
roadmap completion,
critical-risk remediation,
control coverage,
security-review completion,
security exception aging,
incident-response readiness,
security-testing coverage.
This measures whether the security program is actually functioning.
97.29 Security Roadmap Metrics
Useful roadmap measurements include:
Initiatives Planned
Initiatives Completed
Initiatives Delayed
Critical Risks Addressed
Risk Reduction Achieved
Security Debt Reduced
Control Coverage Improved
Completion percentage alone is insufficient.
A completed project that produces little risk reduction should not be considered highly successful merely because it reached its deadline.
97.30 Security Program Health
A security program health assessment can consider:
People
Are required skills available?
Process
Are procedures consistently followed?
Technology
Are controls functioning?
Governance
Are decisions documented?
Measurement
Are outcomes measurable?
Resilience
Can the organization recover?
97.31 Continuous Improvement
A mature security program uses a continuous-improvement cycle:
Assess
  ↓
Prioritize
  ↓
Plan
  ↓
Implement
  ↓
Measure
  ↓
Validate
  ↓
Learn
  ↓
Improve
  ↓
Assess Again
This should be embedded into normal engineering operations.
97.32 Post-Incident Improvement
After an incident, the organization should ask:
What happened?
Why did existing controls fail?
Which assumptions were incorrect?
Which detection opportunities were missed?
Which processes slowed response?
What architecture changes are required?
How will the fix be validated?
The objective is not simply to close the incident.
The objective is to reduce the probability of recurrence.
97.33 Blameless Security Learning
Incident analysis should focus on system improvement rather than personal blame.
For example, instead of:
Who made the mistake?
ask:
Why did the system allow this mistake to create a security incident?
This can reveal:
unsafe defaults,
inadequate permissions,
missing validation,
poor documentation,
weak monitoring,
insufficient testing.
97.34 Security Knowledge Management
Security knowledge should be retained in an accessible organizational system.
Useful artifacts include:
architecture diagrams,
threat models,
policies,
incident reports,
security decisions,
control documentation,
testing results,
risk registers.
This reduces dependency on individual employees.
97.35 Security Risk Register
The security program should maintain a current risk register.
Typical fields:
Risk ID
Description
Asset
Threat
Likelihood
Impact
Current Controls
Residual Risk
Owner
Treatment
Due Date
Status
Review Date
The register should be actively maintained rather than created only for audits.
97.36 Risk Treatment
Each significant risk should have a treatment strategy.
Possible options:
Avoid
Remove the risky activity.
Mitigate
Implement controls.
Transfer
Shift some financial or operational impact to another party.
Accept
Explicitly accept the remaining risk.
Risk acceptance should be deliberate and authorized.
97.37 Security Portfolio Management
A large security program may contain dozens of initiatives.
Portfolio management helps avoid:
Projects should be evaluated as a portfolio rather than independently.
97.38 Dependency Management Between Security Projects
Some initiatives depend on others.
Example:
Central Identity
      ↓
Strong Authorization
      ↓
Privileged Access
      ↓
Tenant Isolation
      ↓
Advanced Audit Controls
Starting downstream projects before foundational controls can create rework.
97.39 Security Architecture Foundations
Certain capabilities should generally be treated as foundational:
Higher-level capabilities depend on these foundations.
97.40 Security Program Change Management
Security programs themselves change.
Changes should consider:
Security governance should therefore adapt without losing accountability.
97.41 Security Communication
Different audiences require different communication.
Engineers
Need:
Managers
Need:
risks,
priorities,
resource requirements.
Executives
Need:
business impact,
strategic risk,
decisions required.
Auditors
Need:
evidence,
control descriptions,
test results.
Effective security communication translates the same underlying evidence into audience-appropriate information.
97.42 Security Culture
A strong security culture means security is treated as part of engineering quality.
Indicators include:
developers report security problems early,
teams perform threat modeling,
security testing is normal,
incidents are reported quickly,
security requirements are included in planning.
Security should not be perceived solely as a blocking department.
97.43 Security Champions
A security-champion program can extend security expertise into engineering teams.
Champions can help with:
Security champions do not replace dedicated security teams.
They improve collaboration and security ownership.
97.44 AI Security Champions
AI-heavy teams may also require AI-security champions.
They can help developers understand:
prompt injection,
unsafe tool use,
data leakage,
model limitations,
output validation,
AI evaluation.
This is especially useful when AI capabilities are distributed across many product teams.
97.45 Security Program Automation
Program management can be partially automated.
Examples:
automatic security-ticket creation,
policy compliance checks,
vulnerability SLA alerts,
control-health dashboards,
security evidence collection,
risk-register reminders.
Automation should reduce administrative overhead without eliminating necessary human review.
97.46 Security Evidence Automation
A mature platform can automatically collect evidence such as:
deployment approvals,
vulnerability scans,
access reviews,
configuration states,
backup tests,
security evaluations.
This reduces the burden of preparing evidence manually.
97.47 Security Program Review
Periodic program reviews should examine:
Risk
What changed?
Controls
What failed or improved?
Roadmap
What was completed?
Resources
Are they sufficient?
Incidents
What was learned?
Technology
What changed?
AI
What new capabilities or risks appeared?
97.48 Annual Security Strategy Review
At least periodically, reassess:
business strategy,
threat model,
architecture,
regulatory requirements,
risk appetite,
security maturity,
staffing,
technology.
The security strategy should evolve as the platform evolves.
97.49 New AI Capability Review
Before introducing a major AI capability, perform a structured review.
Example:
New AI Feature
      ↓
Data Flow Analysis
      ↓
Threat Model
      ↓
Trust Boundary Analysis
      ↓
Authorization Review
      ↓
AI Safety Evaluation
      ↓
Security Testing
      ↓
Production Controls
      ↓
Monitoring
      ↓
Approval
This creates a repeatable AI security governance process.
97.50 Security Program Failure Modes
Security programs can fail through:
Unclear ownership
Nobody is accountable.
Excessive bureaucracy
Teams bypass security processes.
Metrics without outcomes
Dashboards look healthy while risks remain.
Roadmaps without resources
Projects repeatedly miss deadlines.
Policies without enforcement
Rules exist only on paper.
Security siloing
Security teams are disconnected from engineering.
Lack of continuous review
Controls become outdated.
97.51 Avoiding Governance Overload
Security governance should be proportional to risk.
A low-risk change should not require the same review process as:
a new privileged agent,
a new customer-data pipeline,
a new external model provider,
or a major tenant architecture change.
Risk-based governance improves both security and engineering velocity.
97.52 Security Program Operating Model
A practical operating model can be:
Security Leadership
       │
       ├── Governance
       ├── Security Engineering
       ├── AI Security
       ├── Security Operations
       └── Incident Response
                │
                ↓
        Engineering Teams
                │
                ↓
          Product Teams
                │
                ↓
          Platform Users
Responsibilities should be documented rather than assumed.
97.53 Security Program Maturity Assessment
Assess the program across:
| Domain | Basic | Mature |
|---|
| Ownership | Informal | Explicit |
| Risk | Reactive | Continuous |
| Controls | Manual | Automated where appropriate |
| Metrics | Basic | Outcome-based |
| Roadmap | Ad hoc | Risk-driven |
| AI Security | Limited | Integrated |
| Incidents | Reactive | Practiced |
| Governance | Periodic | Continuous |
| Evidence | Manual | Automated |
| Improvement | Incident-driven | Continuous |
97.54 Security Program Implementation Roadmap
Phase 1 — Establish Governance
Create:
security charter,
ownership model,
risk register,
security policies.
Phase 2 — Establish Roadmap
Identify:
major risks,
security gaps,
priorities,
dependencies.
Phase 3 — Establish Control Ownership
Assign:
Phase 4 — Establish Measurement
Track:
KPIs,
KRIs,
control health,
roadmap outcomes.
Phase 5 — Establish Continuous Validation
Implement:
Phase 6 — Continuous Improvement
Use:
metrics,
incidents,
audits,
threat intelligence,
architecture changes
to continuously update the program.
97.55 Security Program Checklist
Governance
Ownership
Roadmap
Risk
AI Security
Continuous Improvement
97.56 Final Security Program Architecture
A mature security program can be represented as:
                  BUSINESS STRATEGY
                         │
                         ↓
                    SECURITY STRATEGY
                         │
                         ↓
                     THREAT MODEL
                         │
                         ↓
                     RISK REGISTER
                         │
                         ↓
                 SECURITY ROADMAP
                         │
            ┌────────────┼────────────┐
            │            │            │
         People       Controls     Technology
            │            │            │
            └────────────┼────────────┘
                         ↓
                    OPERATIONS
                         ↓
                    TELEMETRY
                         ↓
                     METRICS
                         ↓
                  CONTROL VALIDATION
                         ↓
                  GOVERNANCE REVIEW
                         ↓
                  SECURITY DECISIONS
                         ↓
                  IMPROVEMENT ACTIONS
                         │
                         └──────────→ RISK REGISTER
97.57 Conclusion
Security program management provides the organizational mechanism that keeps security architecture effective over time.
A platform should not rely on informal assumptions such as:
“the security team handles it,”
“the developer owns it,”
“the cloud provider protects it,”
or “we already passed an audit.”
Instead, every important security capability should have:
For AI platforms, governance must extend beyond traditional application security.
It must also address:
The strongest security programs integrate security into normal product and engineering processes rather than treating it as a separate final-stage inspection.
The long-term operating loop is:
Govern → Assess → Prioritize → Build → Validate → Measure → Learn → Improve
When this loop becomes part of normal organizational behavior, security becomes sustainable rather than dependent on individual effort.
End of Chapter 97


Comments
Post a Comment